
Skip to content
View Bor-Code's full-sized avatar

Highlights

  • Pro

Block or report Bor-Code

Block user

Prevent this user from interacting with your repositories and sending you notifications. Learn more about blocking users.

You must be logged in to block users.

Content in all repositories owned by your account will be closed.
Maximum 250 characters. Please don’t include any personal information such as legal names or email addresses. This note will only be visible to you.
Report abuse

Contact GitHub support about this user’s behavior. Learn more about reporting abuse.

Report abuse
Bor-Code/README.md

header

typing

> whoami

Name        : Boran Kızılkaya
Role        : Computer Engineering Student
Domain      : Defensive Security / Malware Analysis / Threat Detection
Platform    : Windows, Linux
Mission     : Build practical security tools for malware analysis, threat detection and Windows telemetry
> focus --areas

> ls ./case-files

CASE 01 — MalwareAnalysisTool

Windows-focused malware analysis tool for practicing static and dynamic analysis.

  • Static inspection of executable files
  • CLI-driven analysis workflow
  • Dynamic analysis flow with timeout handling
  • Structured suspicious behavior and event output

CASE 02 — SentinelFlow

Defensive monitoring project focused on visibility, event analysis and detection-oriented engineering.

  • Collection and structuring of security data
  • Monitoring and visibility first design
  • Blue Team fundamentals
  • Detection logic and analysis workflows

CASE 03 — Detection & Telemetry Lab

Controlled lab for simulating suspicious Windows behaviors and mapping detections to MITRE ATT&CK techniques.

  • Simulate suspicious behaviors in an isolated environment
  • Collect Windows telemetry
  • Map behaviors to MITRE ATT&CK
  • Write detection logic and document findings as case studies

MalwareAnalysisTool SentinelFlow

> stack --list

stack


Python

C++

C

PowerShell

Windows

Linux

> learning --current

learning

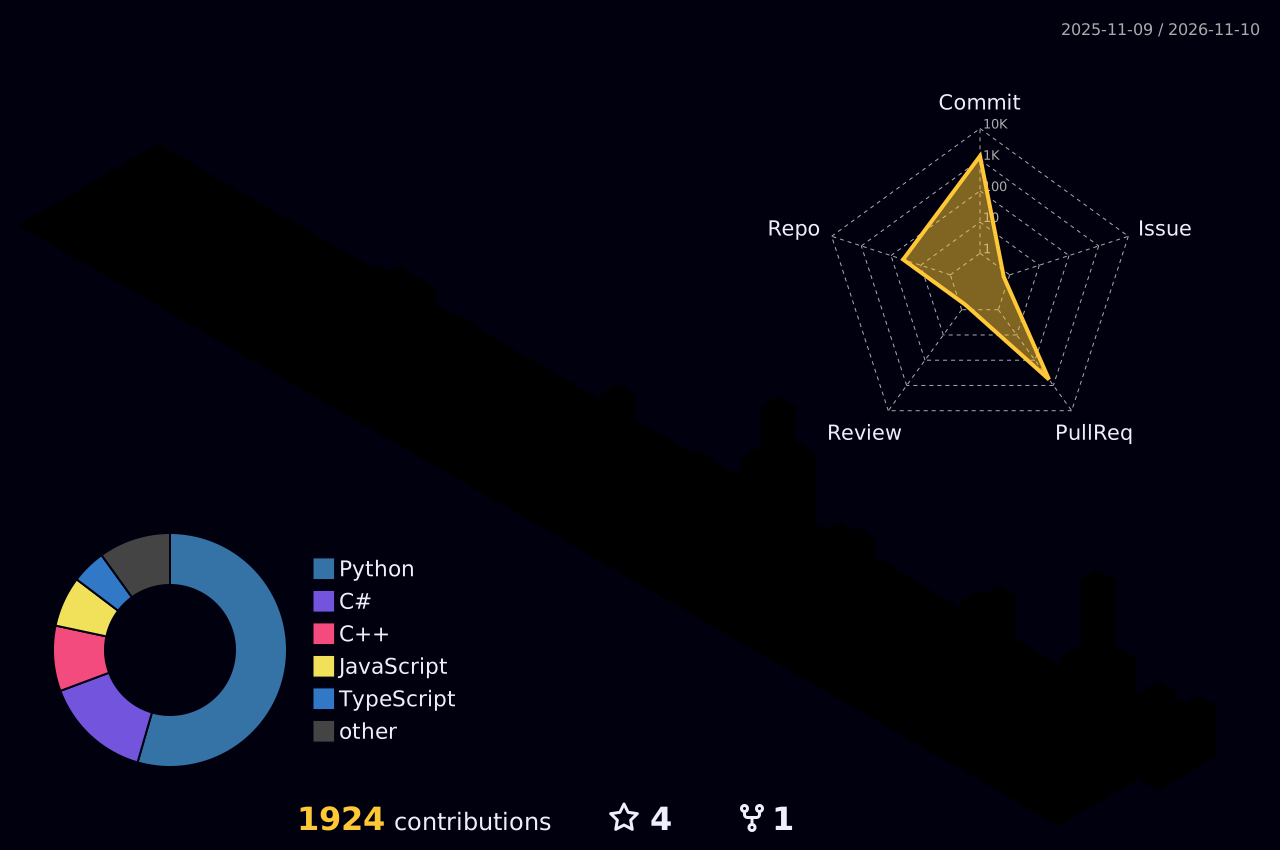
> stats

3d contributions

snake

> contact

footer

Popular repositories Loading

  1. Visual-Waterfall Visual-Waterfall Public

    MVVM mimarisi ile C# ve WPF kullanılarak yazılmış; Big-O analizi, MIDI ses efektleri ve Glassmorphism tasarıma sahip gelişmiş Algoritma Görselleştiricisi.

    C# 1

  2. Bor-Code Bor-Code Public

    1

  3. MalwareAnalysisTool MalwareAnalysisTool Public

    C++ 1

  4. PE-Malware-Analysis-Lab-v2 PE-Malware-Analysis-Lab-v2 Public

    Windows PE analysis and malware analysis methodology labs with static analysis, dynamic analysis, API monitoring, x64dbg verification, and structured reporting.

    C 1

  5. Sentinel-Flow Sentinel-Flow Public

    Advanced Cyber Security Dashboard & Network Analyzer powered by Python & React. Features Real-time Monitoring, 3D Threat Map, LAN Scanner, and Ransomware Shield.

    JavaScript

  6. MicroSIEM- MicroSIEM- Public

    A lightweight, cross-platform SIEM solution for real-time network monitoring and threat detection. Built with Python & Flask.

    Python