





Founder & Systems Builder — DSG ONE
Building the execution boundary for AI agents that need to act on real systems — with authorization, policy, human approval, and verifiable evidence.
Explore DSG ONE ↗ · Production Evidence ↗ · Explore Spacetime ↗ · Public repositories ↗


DSG ONE separates AI planning, authorized execution, and verifiable evidence. Choose the path that matches your goal:
- Understand the platform: DSG ONE website and public Spacetime source.
- Try a scoped CI readiness check: Verified Execution Gate (see the runnable example below). This is not a complete agent E2E test.
- Install the Claude Code governance client: DSG Governance plugin. Review OAuth, permissions, and live route availability first.
- Support open-source maintenance: GitHub Sponsors. Sponsorship does not grant production access or replace licensing.
For release claims, check the dated source SHA, evidence scope and reproducibility limits below. Public documents are not substitutes for private runtime logs or independently verified provider E2E.
Snapshot, not live status: these records apply to the pinned source/image identities and workflow results at the dates shown. A successful CI run does not establish end-to-end behavior of every route.
DSG ONE / DSG Spacetime — evidence-first agent execution. The following are owner-controlled, dated production results, not proof that every AI Agent, device, or customer workflow completes end to end.
Verified release gates:
| Scope | What passed | Evidence |
|---|---|---|
| Spacetime production image | Exact-main CI and Build, pinned source/image identity; ECR scan COMPLETE, 0 findings at inspection | CI #41662202368 · Build #41662202353 |
| Owner-governed production promotion | Owner-protected signed-image workflow and public HTTPS checks | Owner Image Release #41677352169 |
| Second Android Native device | Atomic host activation, 5 additive signed routes in the host contract; original device and peers preserved | Android 13 activation #41678418832 |
| DSG ONE public website | Exact-main CI/Build, separate ECR image with completed zero-finding scan; owner Ship and public serving source-SHA readback | Website CI #41685702936 · Build #41685703027 · Owner Ship #41686912248 |
Pinned release identities (two distinct images):
- Spacetime / Android 13 host activation source:
b8347d175a96613f2f5a628900198bbed4bc6351
Image digest:sha256:3552940f2c26d657dfca634046e066ef5aa94589ee9611a346018e42122067c2 - DSG ONE website Ship source:
8b1954b5178353729da53382c1a9001ed321eecb
Image digest:sha256:12cfc0f03f0ed097977f90d8bcd23d48e66aeb9da9ee3270bb0bd1721309e9e6
Public evidence and independent-review instructions
Public GitBook: Android 13 Production Evidence · DSG ONE verification page · Dated website evidence page · AI-readable Markdown
To reproduce responsibly: start with the public dated GitBook report and compare the listed immutable SHA/digest and workflow IDs; obtain authorized read-only access for private GitHub Actions logs and AWS ECR scan records; then execute separate real bound-device/provider result, wrong-device denial, and Evidence/Replay tests before calling those paths E2E verified. The dated website URLs have source and successful website Ship workflow evidence, but a separate anonymous HTTP 200 check for those exact pages was not independently recorded in the cited audit. Their present availability must be checked separately.
Truth boundary:
SECOND_DEVICE_PROVIDER_E2E=NOT_VERIFIEDin the actual Android 13 activation logs. Workroom Claim → Checkpoint → Resume → real provider reply, external-user isolation, owner human MFA/OTP E2E and full-system Agent autonomy are NOT VERIFIED / PENDING. Private GitHub workflows are not publicly inspectable without permissions. Zero ECR findings is a point-in-time scan result, not a perpetual security guarantee or certification.
For auditors and pilot partners: DSG ONE welcomes scoped evaluations with an explicit plan, allowed provider action, expected result, negative authorization test, and evidence-replay acceptance criteria. We publish what passed, what did not, and what an independent reviewer still needs.
DSG ONE website release: PASS for exact pinned source ccee11e6220af294da39353192622d99844de1b5 and image digest. A third-party no-login Python check actually passed the current public status identity and all nine documented public URLs (10 endpoints total); it did not repeat private AWS/GitHub OIDC authentication.
Release proof and limits (TH/EN) · Public evidence JSON · Runnable Python verifier
Truth boundary: v1.3.0 is still NOT RELEASED, and Workroom Claim→Checkpoint→Resume or entire Agent/Native/Cinema E2E is NOT VERIFIED. The archived v1.2.0 DOI below is unchanged.
Verified publication/archive, not independently reproduced public Production E2E. The public evidence package is DSG Spacetime v1.2.0, published on 30 October 2026. This is the latest publication verified in the linked public records as checked on 1 November 2026; this check does not represent a new Production execution on 1 November.
OPEN PUBLIC EVIDENCE (TH/EN) · EVIDENCE STATUS AND SCOPE · Machine-readable evidence
| Open and verify | What it proves |
|---|---|
| Zenodo v1.2.0 / DOI 10.5281/zenodo.23796173 | Citable dated public archive |
| GitHub release v1.2.0 | Exact public release |
| Release integrity / 24-file verification | Reproduce archive checksum and signed-commit API checks |
| Production evidence and limitations | Scoped read-only NVIDIA Workroom/browser/Memory acceptance; private-primary-record limitations |
| Public reproduction protocol | Which checks are public, access-restricted, or still unverified |
| Publication status | Release commit, SHA-256, archive ingestion and date |
Truth boundary: the specified NVIDIA Nemotron API read-only Workroom/browser/Memory slice is documented against a pinned source and serving-image digest. Original production execution records and the Ed25519 CI payload remain private. No independent public Production E2E replay, arbitrary device execution, or current universal agent success is claimed. More recent development activity is not automatically a new public evidence release.
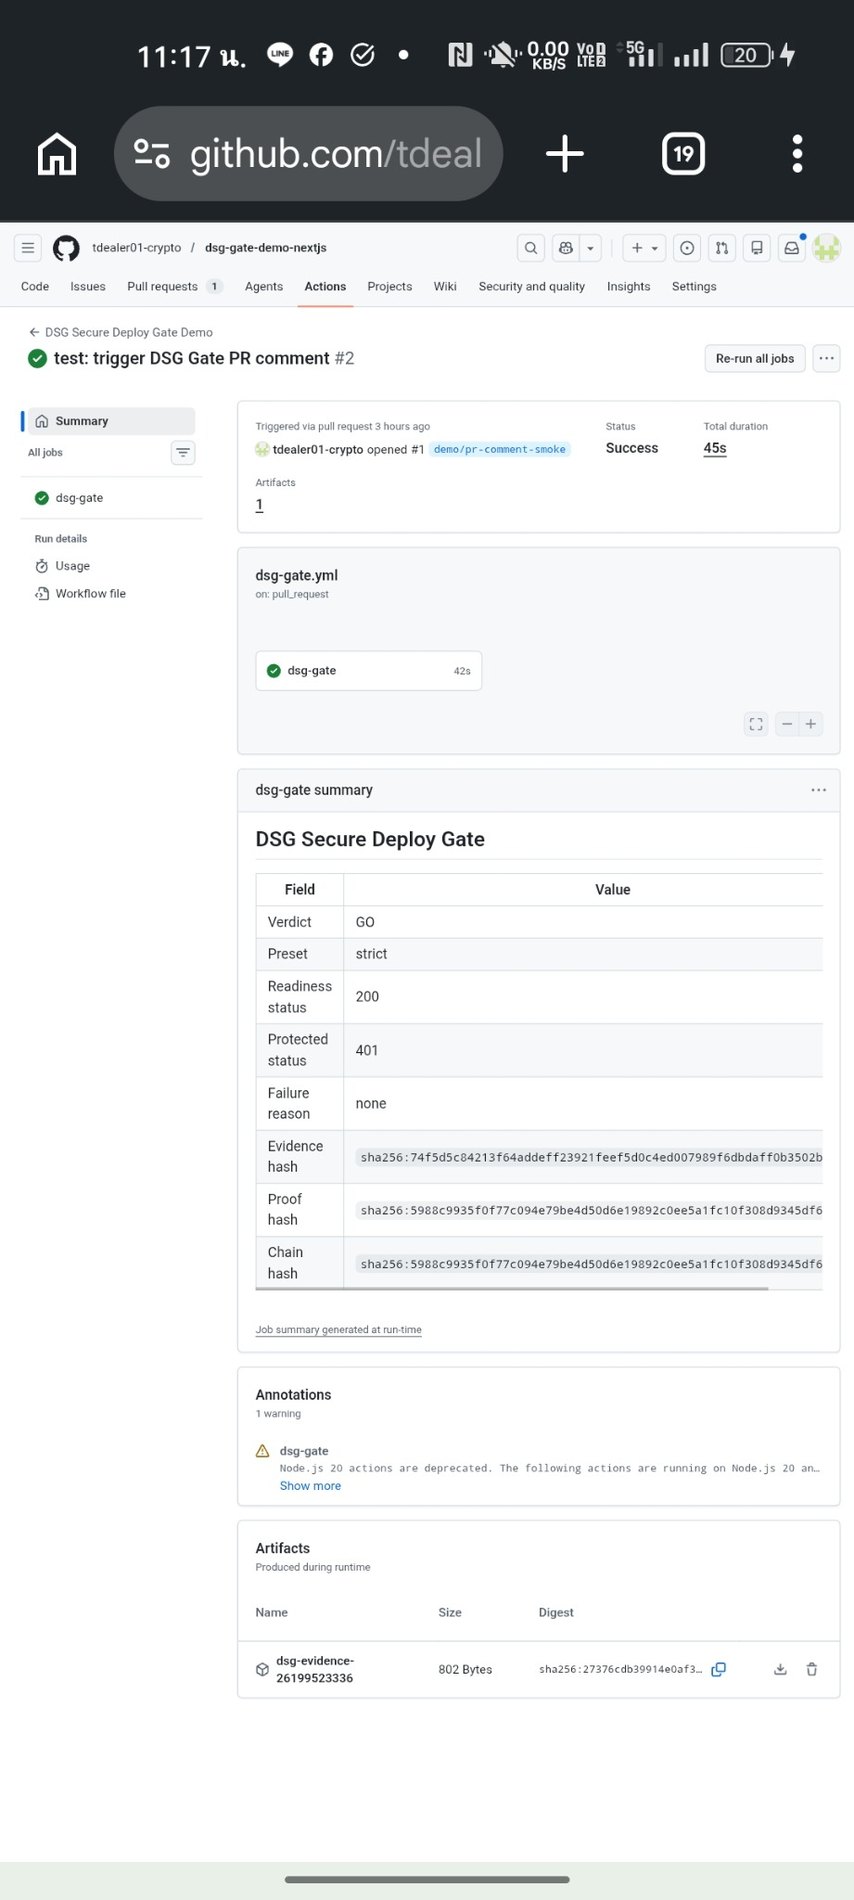
View the real GitHub Actions demo repository · Verified Execution Gate documentation
The image is an existing GitHub Actions demo screenshot, not a new live Production E2E recording. A verified 10-second Production GIF is not published; one should only be added after a real capture has been reviewed and sanitized.
Quick Start (GitHub Actions, v1 readiness check): create .github/workflows/dsg-readiness.yml in a GitHub repository and replace https://your-app.example/health with your real HTTP 200 readiness URL:
name: DSG readiness evidence
on: [workflow_dispatch]
permissions:
  contents: read
jobs:
  dsg-check:
    runs-on: ubuntu-latest
    steps:
      - name: Check readiness with DSG
        uses: tdealer01-crypto/dsg-secure-deploy-gate-action@v1.1.0
        with:
          preset: basic
          readiness_url: https://your-app.example/health
          require_json_ok: 'false'
      - name: Show evidence artifact
        if: always()
        uses: actions/upload-artifact@v4
        with:
          name: dsg-readiness-evidence
          path: dsg-evidence.json
Where to see the result: GitHub repository → Actions → DSG readiness evidence → Run workflow → job result / dsg-readiness-evidence artifact. This tests readiness, not full governed execution. The v1.1.0 Action tag and its input contract were checked against the real repository; do not substitute undocumented CLI commands or an unverified release tag.
Powerful agents should be able to do real work. Their permission to act should never be invented by the model.
DSG ONE is a governed AI execution platform built around a practical separation: models reason; authorization governs; providers execute; evidence records what happened. The aim is autonomous work within an owner-approved plan, not a pile of confirmation dialogs and not an agent with unrestricted tool access.

The decision belongs at the execution boundary. Within an approved scope, ordinary steps can proceed. If authority is missing or an action crosses its approved boundaries, the system must stop rather than improvise permission.
| Project | What it is |
|---|---|
| DSG Spacetime | Public source for plan-bound authorization, governed tool routes, execution and tamper-evident evidence. |
| DSG OS + Cinema | Governed browser and shared-screen execution work, with policy, approval and proof boundaries. |
| DSG ONE / App Builder | Application and workflow surface for agents operating under governed plans. |
| Verified Execution Gate | GitHub Action for bounded execution decisions and proof receipts. |
| DSG Control Plane | Public control-plane implementation and interface work. |
| 01 — Autonomy with a scope Let an agent carry out work inside the user's actual authority and the approved plan. |
02 — An enforceable boundary Evaluate plan, principal, permissions, policy and required approvals before provider execution. |
| 03 — Evidence, not confidence Keep provider results, hashes and signed or replayable proof where the implementation supports them. |
04 — One understandable experience Make task state visible as |
VERIFY     → inspect actual state and authoritative evidence
AUTHORIZE  → exact plan, real principal, correct scope
EXECUTE    → governed provider route; never a model bypass
PROVE      → record what the provider actually returned
RECOVER    → explain failure and the next valid action
Areas of work: agent orchestration · Model Context Protocol (MCP) · deterministic policy · Z3/SMT verification · cryptographic evidence · secure deployment · browser automation · TypeScript / Python · AWS.
Public repositories contain implementation details and dated, scoped evidence. A passing CI job, healthy service, signed read-only call or successful component test does not establish complete production E2E. In particular, do not infer full approved browser connect/execute, device control, XR runtime acceptance or independent compliance certification from this profile.
For source-specific progress and limitations, review the linked repository documentation and associated run evidence. Private customer data, infrastructure secrets and proprietary runtime materials are not presented here.
DSG ONE website · Open-source work · Spacetime architecture · Sponsor
Built in Thailand · Designed for interoperable AI systems · Evidence before claims.
ภาษาไทย — เกี่ยวกับ DSG ONE
DSG ONE พัฒนาระบบกำกับการทำงานของ AI Agent เพื่อให้เอเจนต์ดำเนินงานจริงภายใต้สิทธิ์และขอบเขตที่เจ้าของอนุมัติไว้ โดยใช้ DSG Spacetime ตรวจนโยบายและการอนุมัติก่อนเข้าถึงเครื่องมือหรือผู้ให้บริการจริง และบันทึกหลักฐานผลการทำงาน
แนวคิดหลักคือ ให้ AI คิดและเสนอแผนได้ แต่ไม่มีสิทธิ์สร้างอำนาจอนุมัติขึ้นมาเอง งานที่มีสิทธิ์ให้ดำเนินต่อได้ งานที่เกินขอบเขตต้องหยุด พร้อมแจ้งเหตุผลและวิธีแก้ไข
ข้อมูลการทดสอบของแต่ละส่วนต้องพิจารณาตามหลักฐานและขอบเขตที่ระบุไว้ ไม่ใช้ผลทดสอบบางฟีเจอร์แทนการยืนยันว่าทั้งระบบผ่าน Production E2E